

The platform
Change the algorithm, not the system
Discovery tells you where the cryptography is. 4Quays is what changes it safely, under central policy, without every team re-implementing an algorithm of its own.
01Observe
Observe
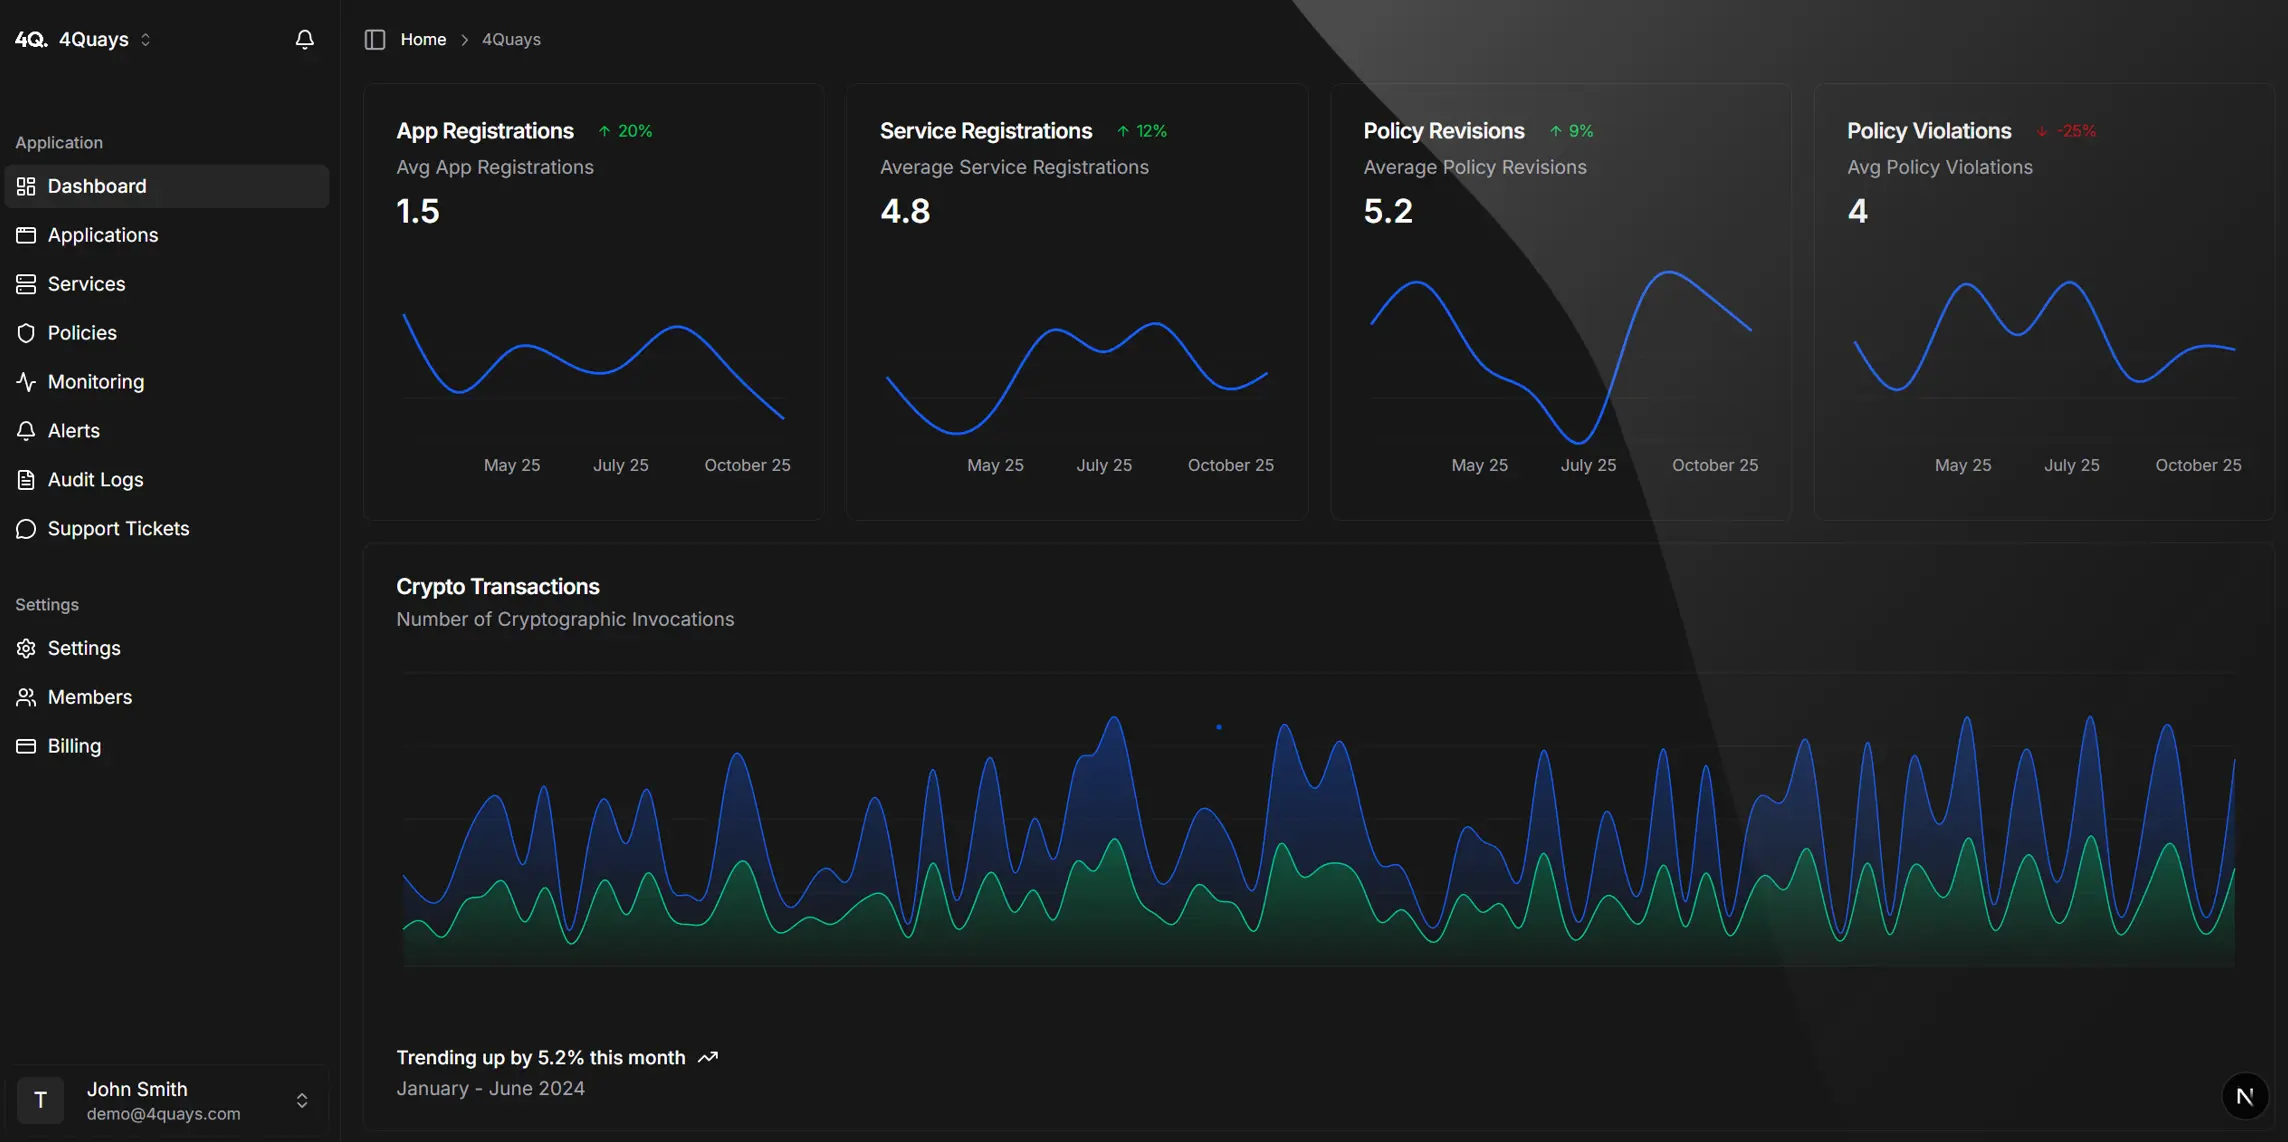
Import and discover cryptographic assets and dependencies across connected environments, giving you a live inventory (CBOM) instead of a stale spreadsheet.
02Execute
Execute
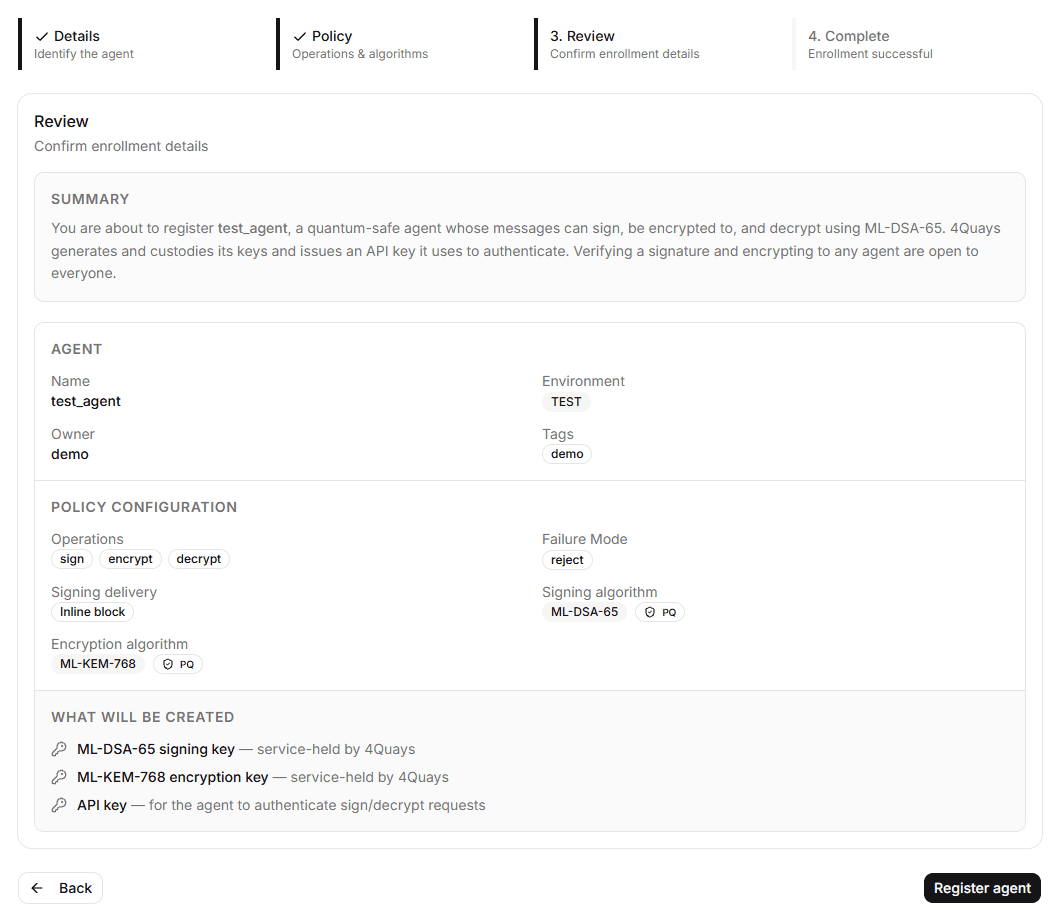
Orchestrate approved cryptographic change through supported APIs and agents. After the initial integration, your teams don't implement each new algorithm themselves.
03Govern
Govern
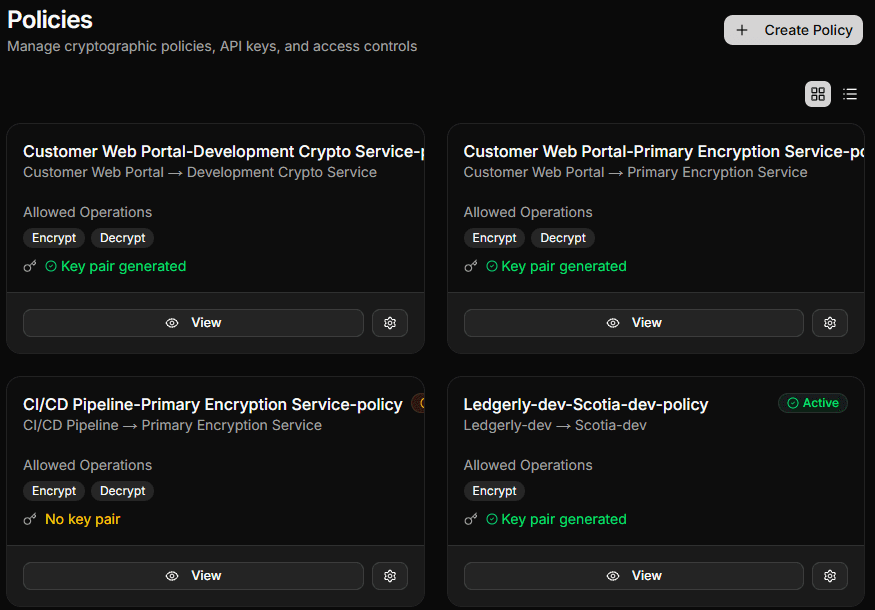
Define central policy over algorithms, keys and providers, whether classical, hybrid or post-quantum, decided centrally rather than per team.
04Prove
Prove
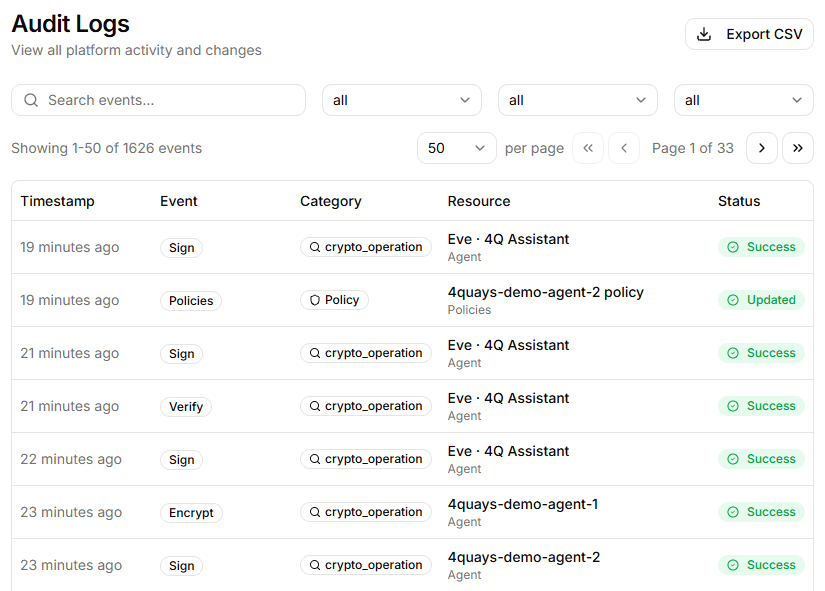
Monitor, audit and remediate continuously. Evidence flows into your SIEM and audit workflows, with controlled rollback if anything misbehaves.
See how it works
See it work
A four-minute walkthrough: discovering cryptographic assets, defining policy centrally, and migrating a live service to ML-KEM-1024, without the application ever touching key material.
- 01
Discover the estate
Connectors pull cryptographic assets out of cloud, code and network sources into one live inventory.
- 02
Define policy centrally
Permitted algorithms, keys and providers are decided once, centrally, instead of per team.
- 03
Enroll a live service
A running CI/CD service is brought under policy without being rewritten or redeployed.
- 04
Migrate to ML-KEM-1024
4Quays generates and manages the key, the application never touches key material, and a CBOM entry is created automatically.
Integrations
Connected to the systems you already run
Discovery reaches into cloud key stores, source control, network and endpoint telemetry, and the AI agent platforms your teams are adopting. Operations, audit logs and alert events forward back out to your SIEM.
Cloud and key stores
- Azure Key Vault
- AWS KMS, ACM and Secrets Manager
- Google Cloud KMS and Secret Manager
Source and supply chain
- GitHub
- Bitbucket
- CycloneDX import
Network and endpoint
- Cloudflare Zero Trust
- Zeek
- Microsoft Defender
- FleetDM
- Qualys CertView
AI agent discovery
- AWS Bedrock Agents
- OpenAI Agents
- Azure AI and Entra Agent ID
- Agent frameworks in source
SIEM and observability
- Splunk
- Microsoft Sentinel
- Sumo Logic
- Datadog
- Elastic
- IBM QRadar
- CrowdStrike Falcon LogScale
- Generic webhook
Agent and developer
- MCP server
- TypeScript SDK
- Signing hooks
- Public verify API
AI
On both sides of the problem
AI is on both sides of this problem. It is another surface to protect, and it is part of how the control plane does the protecting.